2016-03-19

A Way forward in developing the key capabilities of Nation Defence in Finland by using Enterprise Architecture views

A WAY FORWARD


The strategy for the FINDEF was first to create an enabling ICT structure that would provide leverage to process rethinking and integration. The third phase was to build new capabilities required in National Defence. The sequential strategy was based on the understanding that strongly siloed ICT structure was preventing information and processes from integration. Further, there was understanding that without platforms to develop integrated processes and shared information environments, there were no gains achieved in developing asymmetric military effects illustrated in Figure 36. 

By 2008, the first phase was achieved, and the description of enabling ICT structure as part of the defence system in Finland was described as a nationally defined service platform for common and joint processes. The technical structure included core network that connected data centres providing application and content services accessed via access networks. Tactical level field networks were connected to nation level structure via connection points.


Figure 36: Simplified model for improvement strategy for the Finnish Defence Forces 2004

This writing was focusing on the first phase - transforming the ICT structure so that it would enable further proceedings in developing common and joint functions of military affairs. The transformation of ICT structure in Finnish Defence Forces 2004 – 2008 was following basic lines of evolution in using ICT to support military strategic and operational functions as pictured in the following Figure 37. The evolutionary model for ICT application includes interrelated layers of Networking, Computing, Information Security and Information Management. 

On 2004, the Finnish Defence Forces were using transport networks based on Synchronous Digital Hierarchy in connecting garrisons and command posts together. Computing and communications services were provided mainly within local areas and branches in each garrison. Each garrison created a local domain that was loosely connected to other garrisons enabling data sharing. Information security was based on ownership of physical and technical domains. It was trusted since it was operated and developed under each line command: North, East, West, Air and Navy. Connecting the trusted domains to other domains was untrusted. Unstructured official and unofficial digital information were produced in files created in various formats and stored in Folders managed mainly by individuals. For sharing of information, there were some shared Folders and disks accessible to carefully defined users. Most of the files were shared by intranet electronic mailing system between individuals.


Figure 37: The journey of the FINDEF 2004 – 2008 on the roads of evolution of Military ICT usage

The transformation accelerated the ICT structure to the level where networks were specified supporting more centralised computing and multichannel access. Computing was based on virtual infrastructure providing both distribution for survivability and flexibility for new requirements. Information security was based on a trust in systems as they were more controlled, end users were separated from services, and there was a structure for defence in depth built. The file oriented information management culture was gradually moving via page sharing to more real-time sharing culture of enterprise social media.

The transformed ICT structure enabled the major change of the Command structure of the Finnish Defence Forces. There remained only three commands: Land, Maritime and Air. The National University of Defence provided a level of academic knowledge and education needed in Force Production and specialised units directly under the Defence Staff were providing unified support to all Commands.  

Defence Forces had taken its first step towards process supported matrix and virtual enterprise. The step was enabled by new ICT structure dividing Military Affairs into four domains of shared information: Tactical, Operational, Support and Public. The domains are described in Figure 38.


Figure 38: Information domains of the Finnish Defence Forces 2008

Tactical domain remained further divided into Intelligence, Sensor, Fires and Land Forces deployable field networks. OPNET provided a platform for nationwide military missions at operational and tactical levels. Tactical domains were connected to OPNET providing interoperability and coordination required in joint and combined operations between Services, Allies and other Governmental Agencies. HALNET and INET were connected in a way that enabled establishing the Force Production and Support in the more cost-effective manner by using example strategic partners for Logistics and Training.

The four domains provided Information Environment to further process development in all three military areas: Force Utilization, Production and Support. The ICT infrastructure enables information flow within the Defence Force but also between its key partners. A basis for more efficient National Defence value chain illustrated in Figure 39 was created. Further papers will explain proceedings at the process level and the development of Land Forces Tactical domain on their journey towards a new strategic basis for National Defence.


Figure 39: The 2008 platform created with ICT structure for developing essential capabilities in Military Affairs of Finland


This is the final paper in the series of eight (A - H) studies describing how the ICT structure of the Finnish Defence Forces was transformed before 2008.

2016-03-13

Architecture for Information Management Transformation; Part G of Introduction to ICT rationalization program of the Finnish Defence Forces from Enterprise Architecture viewpoints

TRANSFORMING THE ARCHITECTURE OF INFORMATION MANAGEMENT


STARTING FROM BASICS


The digitization of unstructured formal information had started already in early 1980’s in the Finnish Defence Forces. First there were Personal Computers introduced to replace typing machines. Then, at mid-1990, the first digital content management system was implemented to capture both personal emails and formal correspondence together with the publication of standard operational procedures. The system was based on Lotus Notes in the beginning and included taxonomies and metadata models for all formal unstructured information exchange and records keeping within the FINDEF. There was a demand in early 2000 to update the content management system and migrate from Lotus file types towards Microsoft files. The main driver was to achieve interchangeability between other stakeholders. 

The same time, there was a need to update the whole content management system. Thus, a roadmap for migration of file types was created starting from early SmartSuite version 4 evolving through Office XP towards more open file types based on eXtensible Markup Language, XML. The roadmap is illustrated in Figure 31.


Figure 31: A roadmap for migrating the file types for unstructured content within the Finnish Defence Forces

There was a migration window for all legacy file types from SmartSuite version 4 to most current version 9.8 defined. The migration window pushed all content towards one format, SmartSuite 9.8, which was to be supported in read-only function until 2008. All earlier versions together with their applications were cancelled by 2005 (version 4) and 2006 (version 97). The simplifying of office suites also helped in cutting the local support and providing a more stable configuration in workstations. The Microsoft Office 2003 version was defined to be the first family of file types providing a path towards next MS Office versions and more open file types that enabled publication of content as well as archiving better that proprietary file formats.

New file formats opened integration opportunities in IBM Domino, SAP and IBM WebSphere platforms as they were introduced as part of process integration programs in Enterprise Resource Management and C4ISTAR implementation. Integration improved the transferability between unstructured and structured data.

RECOGNISING SITUATION OF THE MATURITY IN CONTENT MANAGEMENT


When the maturity of content management was assessed in the FINDEF, there were three main levels found pictured in Figure 32.  The lowest level was based on individual interests, separate ways of working and personal applications in personal computers that stored personal files. Individualism was recognized the hardest cultural boundary to break as some of the Branches and Units within the FINDEF were using Confidentiality as an excuse not to share any information.


Figure 32: Measuring the maturity of content management in FINDEF

The second level of maturity was found in teams and units that were competing against each other, sharing within the team but not elsewhere and sometimes having surprisingly advanced applications to manage their files. There were many closed workplaces established in Lotus Notes platform; each  Unit had their intra-web page for internal publications, and closed networks hosted shared drives for restricted content.

The third level of maturity found was Defence Forces wide. Official letters, records and standard operational procedures were captured in common parts of Lotus Notes.  People were thinking disseminating information beyond their particular department or team. There were some attempts to share instruction and training content between Defence Schools and Units of Force Production. There were repositories for forms and templates to assist in writing more structured letters and orders. Official letters were accessible to all authorised personnel back to three years in time.

Since the variance in content management culture was found wide, a significant threat was detected for process integration. Thus, ICT rationalization program was tasked to enable the acceleration of content management maturity. The acceleration intention included following goals:
• Enable social communication
• Enable more formal publications
• Enable content sharing with stakeholders outside of Defence Forces 
• Improve the confidentiality of content through all sharing and exchange transactions
• Enable content transformation between unstructured and structured repositories 
• Build ability to improve formal and structured data exchange between all relevant stakeholders.


ENABLING PROCESS INTEGRATION AND MATURING THE CONTENT MANAGEMENT


TIERA implemented tools and services to improve communication between people and machines as well as the maturity of content management as defined in Figure 33.


Figure 33: Enabling communication and content sharing in the FINDEF

Social communication between people was enabled with Collaboration tools like IBM SameTime. It enabled people to have virtual meetings by sharing presentations, white board and exchanging opinions both in voice and chatting. The collaboration was later enabled also with Video Tele-Conferencing, VTC service between all Units. VTC also enabled unintended signals, body language, included in virtual meetings. These enablers were used 2010 when remote work was officially allowed in Defence Forces. People were permitted to work from the nearest garrison rather than commuting through half the Finland every day.
As telephone devices were taken away from desks, the Computer Telephony Integration in SameTime enabled better awareness of presence and conference meetings. Intranet chatting was also adopted quickly by personnel for informal communication while working. 
Shared folders and web pages were substituted with two portals both for Administrative and Operative Environments. People were recommended to publish content on those platforms rather than in their restricted web pages. Pages begun to capture more content from shared files as HTML editing and publishing become easier.

Content sharing with outside stakeholders was improved by creating digital workspaces to be used in integrated projects and development tasks. The official Internet email MIL.FI was secured better, accessed directly from Intranet workstations and file transfer was allowed in controlled manner to get rid of private file sharing with memory sticks.

Similar file sharing was enabled online between Administrative and Operative Environments to have control over the content that flows between confidential levels. Filters and content screening was applied in gateways for monitoring purposes. Enabled official file sharing gradually throttled the informal file sharing and security improved.

As SAP was extended to be the Enterprise Resource Management platform and WebSphere become the portal platform, there was a path created by improving exchange between unstructured and structured data. The Excel-application from MS Office suite was integrated with SAP platform and allowed transfer of data between two worlds. It was imperative that commanding officers were able to extract data from SAP and create reports and presentations quickly and based on factual information. The Word application was similarly integrated with Domino platform and enabled the transformation of Word-document to Domino content.
 

XML-interfaces (XI) were prepared between SAP and the stakeholders along the value chain via electronic message broker. A gateway structure was providing secure and unbroken transactions between nodes in a long chain of value creation. Another gateway was created to allow outsiders access the SAP of FINDEF. The gateway allowed strategic partners to manage essential information on material warehousing and repair. Information integrity was important for the Defence Forces ability to sustain readiness and be able to deploy forces as needed. The third gateway enabled operations abroad to access home services. It was not necessary to establish isolated entities for support systems in operations anymore. The crew in operations focused only on providing battle management system services to troops rather than running administrative support systems. They were provided via global connections from Homeland. See the concept of information exchange between stakeholders in the value chain in Figure 34.


Figure 34: New gateway structure for data exchange between relevant stakeholders in Defence

TRANSFORMING THE CULTURE IN INFORMATION ASSURANCE AND MANAGEMENT


In enabling the cultural transformation of content management in FINDEF, there were three parallel lines of operation adopted: Information Management, Information Assurance and Computing. The transformation to these enablers is illustrated in Figure 35.


Figure 35: Basic plan in transforming information management, assurance and computing in the FINDEF

The line of information management included support to get rid of last paper-based content and migrate towards electronic documents. It was enabled by content integration, collaboration and new publishing services. The second course of action was to migrate from file based content management towards page and database data management. The migration was enabled by publishing services, tool integration and improved information security. The third course of action was to change the feeling from individually owned content towards Defence owned content. It was imperative to change the culture of “need to know” towards “need to share” to build the Defence Forces as learning organization.

The line of information assurance included increasing the awareness of rights and responsibilities to an information user. The user profile means both consuming and creating information. The awareness was established with the integration of security guidance and operations guidance into the same document of standard operational procedures. The integrated procedures made it was clearer to the user, what was possible and what was not allowed. The second course of action was to improve understanding of publishing and accessing information. There was a profound mistrust of people that prevented publication of sensitive information. It was mitigated by showing what role based access management means and providing exemplary behaviour models of improved ways to publish information. The third course of action was improving the awareness in information confidentiality among users. From individual responsibility, the transformation was done towards organizational responsibility for managing content between levels of confidentiality.

The line of computing included improved access, identity and role management. It enabled an access both for strategic partners and via wireless access. Identity was uncoupled from terminal devices, and Microsoft relied on functions. A full smart card based identity management was introduced together with Single Sign-On, SSO feature in making the life of end users easier but simultaneous the access more secure. Assured identity was transferred to role management instead of applications. Role management provided an underlying layer to manage different roles and their rights to access services and use information. It was possible to differentiate individual and his roles in peace time and war time. Definition of roles become a responsibility to superiors and organizations. Human resources were accountable for issuing smart cards to true identities. A Chief Information Officer was responsible for the whole in each Unit of Defence Forces. 
System administration was linked to service management and extended with role and identity management with rigorous implementation of ITIL-processes and IT-service management system. The integrity of services and availability of information become a driving force for ICT Service Provider organizations together with information security.

This ends the series presenting the Transformation of the FINDEF from Enterprise Architecture viewpoints but the conclusion still to be published!

2016-03-04

Architecture for ICT Service Management; Part F of Introduction to ICT rationalization program of the Finnish Defence Forces from Enterprise Architecture viewpoints

ARCHITECTURE FOR TRANSFORMATION OF ICT SERVICE MANAGEMENT AND PRODUCTION


STRATEGY FOR TRANSFORMATION

The FINDEF had IT Management distributed to all its units, and each provincial command had a provider for communication services before 2004. All ICT was mixed as same units were providing both tactical, operational and strategic services. A strategy was defined to consolidate gradually existing structure and then specialise and network towards future in creating more core value to information enabled Defence Forces.  This transformation is depicted in figure 26.


Figure 26: a plan for transformation of ICT service production in the Defence Forces of Finland 2004 

From all distributed and organic ICT units, the first step was to consolidate them under one umbrella of ICT service provider for all operational and strategic services. Only tactical ICT remained with Services and units. The Services (Air, Navy, Land) also became ICT service providers as tactical services were also delivered in the operational and support domains. The consolidation also prevented hasty and sub-optimized decisions of outsourcing as single units were facing a lack of human resources.

The consolidated in-house ICT service provider, C4I Agency, was then planned to network and co-operate with other providers of ICT services in the public sector and also with major telecommunication service providers in the private sector. The networking was after increased cost-efficiency while using the whole weight of the FINDEF ICT budget. There was also some out-sourcing done while ICT infrastructure was transformed. The telephony was outsourced to two operators: Erillisverkot providing TETRA -trunk radio services  and Telia-Sonera providing GSM-services. Partnering with them also accelerated the maturing process of the C4I Agency. 

As the professionalism of ICT service provider was improving more production responsibility was given to it. The Services were tasked to provide tactical information services in tactical domains, but the C4I Agency was ordered to provide them in operational domain. So Land Command became a sub-provider to the C4I Agency, who provided Army Command and Control Information System as a service to all troops that were operating on land. The sourcing steps gradually matured the capabilities of ICT providers for network operations in the time of war.

The final step in ICT business strategy was to improve the National Co-operation in crises times by providing common operational information to key agencies within the Government. The C4I Agency then provided service to Police, Border Guards, Customs, Civil Defence and all ministries. The new segments of users also provided more volume for ICT services, ensured critical mass and helped to sustain both competence of people and negotiation status with vendors. There was also a plan to partner with other service providers. The Enterprise Resource Management system built on SAP-platform was decided to be a joint venture with prominent SAP service providers  as the FINDEF did not have enough flexibility in their policy of hiring high-level IT-experts. The other dimension for partnering was considered to be in basic network services when the initiative for government network was launched by the Ministry of Finance. 

MATURING ICT SERVICE PROVIDER CULTURE AND PROCESSES


The transforming ICT business architecture called after maturing service operations and culture. There was a vision that ICT would be gradually considered as an enabler for improvement and finally a bringer of new opportunities for the core military affairs instead of considered only as support or worst case just a cost item. The vision in Figure 27 was based on a gradually improving understanding of information and its value for military affairs. As the value of information increases, the focus turns towards information and knowledge management. Technology turns into an asset for Command, Control and Information. The information defence becomes essential as the value and dependence increases. 


Figure 27: The vision and Journey for maturity in ICT Service Production in the FINDEF 2004

The journey towards the end state defined in the vision started from very low-level goals in improving existing system management capabilities. The movement towards process and team based working was launched substituting the way where isolated individuals were doing heroic deeds. With new ICT system management technology some manual functions and processes were also automated. 

The second step included steps towards more mature value chain management in all C4I matters. The relationship between provider and client needed more trusted foundation. The cost awareness and cost projection required to be established in Enterprise Resources Management. There was a degree of force behind this change since new requirements were expected to rise during major change of Defence Forces towards 2008.

The third step would bring C4I Agency to level that it would be up to the level with other Service Providers. Teams inside Agency needed also be more responsible and connected with other to shorten the reaction time and improve efficiency in process based service delivery. There was also need to clarify the differences between ICT Management and Information Management as the role of Chief Information Officer was introduced in each unit.


BUSINESS ARCHITECTURE AND MARKET SEGMENTS FOR ICT SERVICE PRODUCTION


As the Defence ICT transformed and matured towards the vision, there was a need to define market segments and specific business strategy for each segment. The six main segments illustrated in Figure 28 were:

  • Administrative customers within the Finnish Defence Forces included all units within FINDEF in their peacetime role
  • Operational customers within the Finnish Defence Forces included all units within FINDEF in their crisis time role and units of other government security agencies
  • Other Security Agencies via Security Network Operator as TETRA mobile service.
  • Other governmental entities via the IT-centre of the Government mainly with IT related services.
  • International operations either via NATO ICT-service provider or Crises Management Office, CMO (intended avenue for further United Nations Operations)
  • Open ICT-market via commercial service providers (mainly telecommunications related services).


Figure 28: The business and market plan for ICT service provider of FINDEF 2004

All ICT services were delivered with metrics for quality and cost. They were measured by agreements, contracts or objectives defined with clients in each market segment. Service Level Agreement, SLA was typically used within Defence Forces, where costs were transferred but there was no in-house billing in place. Service Level Contract, SLC was used with other service providers when money was transferred against delivered value. 

There were different pricing and billing policy in each segment because of their market status. Within government only direct costs were charged. The value creation of open market was tightly controlled by the law preventing the distortion of private markets with public financing.

Besides the pricing and different quality of service attributes, all services to each segment were produced in the similar process, which simplified the actual ICT service production. Network connections between air defence radar stations for the Air Force were provided the same way as connections between TETRA base stations for the SECNET operator.
There were two main ways to provide the service: centralized and distributed. The centralized meant that there was only one unit providing that service. The distributed meant that several regional units were providing ICT services in their particular area of responsibility. 

The ICT value chain included sub-providers both in-house FINDEF and outside of Defence Forces. They were bundled in as channels and integrated by contracts and processes. Architecture Team was taking care of the interoperability through changes and migrating in new systems. Business Team was taking care of advising in contracting, vendor management and measuring value through the chain.

Development of new ICT features was accomplished through Development Department. It managed several integrators that were assembling material, information and programs together before delivering them to C4I Agency for final integration.


TRANSFORMING THE ROLE, RESPONSIBILITY AND MINDSET OF LOCAL CHIEF INFORMATION OFFICER


With rationalization of ICT structure and service production, the role of local ICT unit changed the most. The local Chief of IT or Technology or Signals that used to manage the whole stack of technology, administrators, operators, end users and their information changed within few years as depicted in Figure 29.


Figure 29: The role and responsibility of local Chief of IT before rationalisation 2004

The workstations and terminals were provided as service and the only thing remaining was to monitor the quality and cost-efficiency of working tools. All servers were consolidated to C4I Agency together with their administrators. All applications were provided as service, so only their usage and cost-efficiency remained under local responsibility. All cabling, networks, exchanges and their operators and technicians were transferred to the C4I Agency and provided as service to units. Even ICT service support was rationalised with ITIL processes and accessed via phone and trouble ticketing systems. Problems with workstations were solved online with remote access. The once so great manager for IT and Technology was suddenly left with no job or responsibility – or so it seems at a quick glance.

The new role of Chief Information Officer, CIO was created. She turned the focus from technology towards information, users, and processes to provide benefits. As C4I Agency provided all ICT assets as service from cable installations to applications, there was but planning, ordering and monitoring left for CIO in managing technology. She was supported by Liaison Officer from C4I Agency, who helped in transforming the items in ICT Service Catalogue to valuable services for her unit and agreeing on all this in Service Level Agreement as illustrated in Figure 30.


Figure 30: The new role of Chief Information Officer after 2006

Then the actual information management was begun. With improved cost-awareness in technology, there was a foundation to start planning and monitoring the cost-efficiency of the information usage within the unit. Focus was also turned to process improvement and skills development as information was creating more value to core functions of military affairs. The CIO was improving the working habits, ergonomics and productivity of those involved in staff and knowledge working. She also started to pay attention to staff processes and their improvement as the heads of 6 in each Service became more aware of this potential.

The change was major from an individual perspective. People were supported with information, training for further understanding, workshops to create participation and with recognition of successes in change. Some of the former technical chiefs were able to change, but many moved to other responsibilities and gave room to new competencies. The figurative change in gender actually happened in some units.

End of part VI

2016-02-13

Architecture for Information Security; Part E of Introduction to ICT rationalization program of the Finnish Defence Forces from Enterprise Architecture viewpoints

This is the 5th part of article on Enterprise Architecture views in Transformation of ICT in the Finnish Defence Forces between 2004 - 2008.

Architecture for Information Security

Starting from proximity restricted trust model


Before 2004, the FINDEF had followed very typical information security architecture  based on trusted physical sites and encrypted communications between them. The trust model was extended containing more logical levels as forces were deployed over to several bases and shared information assets. The approach was outstretching the physical perimeter control as logical domains extended over several physical sites and risks were increasing. Encryption between sites was approached as the only means to build “fortification” in logical dimension. No major attempt was taken to control what was happening within the physically controlled and logically encrypted cyber fortress even though the environment was flat from a security viewpoint.
  
The domain based trust model was divided into the following security levels:

  • Open or public level was considered typically featuring The Internet, poster, publication and postcard.
  • The unrestricted level was filtered from open level but did not possess any additional hardening or encryption. Military Internet access and service domain was a typical example of this level domain. It was connected to The Internet via Firewalls that were to filter the traffic and protect from malevolent logical outsiders.
  • Basic level was capable of handling restricted and confidential content since the connections were encrypted at Layer 2 level between physically controlled sites. The basic level domains remained physically separated from The Internet and unrestricted level domains. Air Gap featured this separation. Those Services or Branches in Military that wanted their information being separated from others at a basic level applied additional Virtual Private Network encryption in their communications.
  • The extended level was physically isolated from all other levels except one way “diodes” that provided one-way transactional gateways to transfer lower level information to higher level domains. The extended level was providing information management domain for secret digital content. Major features in differentiating this domain from lower levels were additional layer three encryption and constrained amount of people having access to the sites that provided workstations for this domain. Of course, some Services and Branches took their systems to be more secret than the rest in extended level and isolated them at least with a firewall if not physically.

The physically featured trusted domain structure killed all flexibility and mobility intentions and ended up building several parallel systems and domains. One operations centre did have five parallel workstations for each operator with separate access to Internet, Admin, Land, Navy, Air and Intelligence services. The concept of information security architecture of the FINDEF 2004 situation is illustrated in Figure 22.


Figure 22: The concept of information security architecture of the Finnish Defence Forces 2004


The As-Is Information Security Architecture led Defence Forces into situations where:

  • Information flow was unofficially “sneaked” between levels and domains by using transferable mediums like CD-ROM’s and USB-sticks.
  • Headquarters typically downgraded their staff work to manual as official information systems were slow in following them to field exercises and operations.
  • Much secret information was travelling in possession of personnel unauthorised and led to occasions that it was stolen along with suitcases, laptops or memory sticks.
  • Audio communications were not following the information security architecture. It resulted in many cases that confidential information was shared via less secure communications by voice since digital sharing was constrained.
  • One staff officer told after an intensive exercise when chief information security officer did a hot wash up of detected security issues: “It seems that when I am trying to support the troops on the ground, I end up always violating some security controls!”

Security was not aligned with military affairs but become an art itself , and that was not raised by many since confidentiality also was supporting their independence. It was although clear that following existing security architecture would keep the FINDEF from reaching mobility, situational awareness, information sharing, survivability, process integration and other network enabled capabilities. The list of constraints was long enough to the commanders of FINDEF to call the change.

Vision of content-based security


As early as 2002 the US Joint Forces Command (US JFCOM) had a Content Based Information Security (CBIS)  demonstrated as part of their Advanced Concept Technology Demonstration programmes. The CBIS was based on entire different trust base than the previous physical site and network partitioning oriented. There was three new bases of trust introduced:

  1. Information being labelled based on content and then encrypted accordingly
  2. Strong identification, authentication and authorization mechanism based on something that user has, knows and is.
  3. Sharing information based on a match between the content label and user’s security attributes.

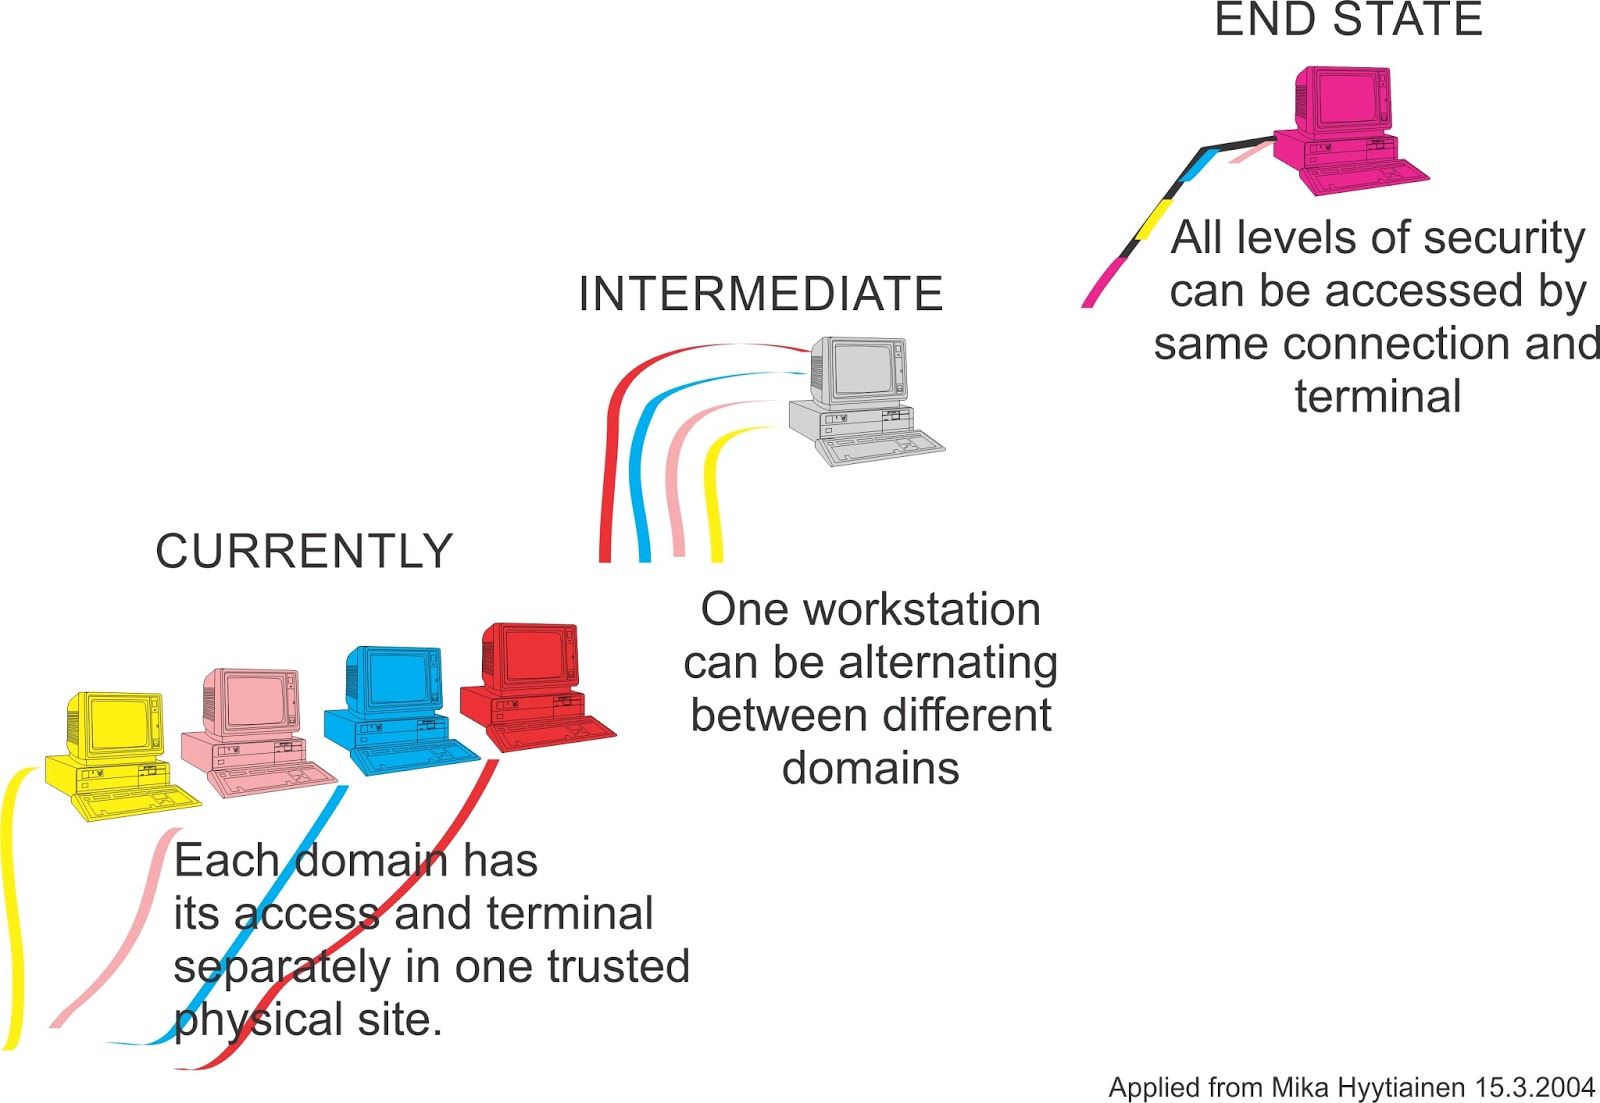
The approach was called information-centric partitioning and trust base was shifted entirely from physical level to logical level. The logical level would be able to provide a road map leading from separate terminals and connections gradually to one terminal with multiple connections and finally to one terminal with one connection as pictured in Figure 23.


Figure 23: Content Based Information Security Roadmap from End User View 

There were the following roles and responsibilities defined in process to suppress the opposition from “need to know” representatives: 

  • Author provides the content to be reviewed
  • Publisher reviews and approves content to be published and defines this with labelling and encryption
  • The reader can access content only defined for his role by the publisher.

There was a strong hope that if US JFCOM can proceed with this approach, they could be the support for FINDEF in the struggle against legacy security policies in NATO.
Unfortunately, the reality overrode the good initiative. U.S. and NATO did not proceed with these ideas until 2009 when it was called after from ISAF operation and then implemented partially in Afghanistan Mission Network. The other threshold on this road was immature content management in FINDEF at a time. The unstructured documents were labelled as files rather than per content. The structured content was labelled only as systems or domains. Analysis of the situation provided a recommendation that content based labelling culture would take too much time to build.

Reality pulls down blue sky intentions


The real solution needed to be found mitigating the maturity of existing content management. It was also constrained by NATO’s legacy trust base. Some system owners, trying to sustain their independence behind “confidentiality” screens, were also to provide a win-win solution. 
The security architecture for realistic TO-BE was defined with following principles:

  • Simplifying security level by cutting them into two: 1. Basic level providing confidentiality from unrestricted to confidential. 2. Extended level providing confidentiality from unrestricted to secret.
  • Getting rid of isolated domains and systems by providing all services through similar Identity and Access Management process based on strong two-factor authentication
  • Mitigating the risk of extended areas of vulnerability by isolating all workstations from server domains
  • Providing lower security level services by virtual desktop constructions
  • Having each domain supervised by security monitoring and controlling function.

The concept view for Information Security architecture of the FINDEF end state was defined as pictured in Figure 24.


Figure 24: A View to the security architecture of FINDEF end state

The workstations at a basic level were isolated from servers and databases by a firewall and access control. The only session-based virtual private connections were allowed to enter access point. All information was consolidated to databases and hard disks in data centres. Internet services were provided to basic level workstations via remote access to virtual desktops running on the Internet side.

The laptops at the extended level provided mobility of terminals and together with a connection access up to secret level applications and information.  The terminal was stripped to as lean as possible and disabled from all unnecessary features. The browser and Virtual Private Network client were the only fat applications in the terminal, all other were provided from Portal or systems beyond it. Authentication provided access to role manager and role defined the screens and services available. All legacy systems were isolated and accessed only via remote sessions to virtual desktops. Several parallel access networks provided assured mobility to extended level terminals together with IP roaming feature. A more technical view of extended level information security architecture is presented in Figure 25.


Figure 25: A technical view of Information Security Architecture from access viewpoint

Above mentioned architecture provided the mobility, flexibility and multilevel security required by new strategy but it also sustained legacy services in isolation sufficient for the purpose, kept apart full Internet connections and enabled digital transfer of content between domains in a controlled manner. The “sneaker network” vanished itself since digital sharing and storing was made so much easier within computing “cloud”. The solution did not require labeling maturity of full content based security but got rid of all but two workstation on the same desk.

Next part will explain the ICT Service management and operations transformation

2016-01-09

Transformation of command post structure; Part D of Introduction to ICT rationalization program of the Finnish Defence Forces from Enterprise Architecture viewpoints

This is the 4th part of writings on transformation of C4I of FINDEF by using architecture models.

ARCHITECTURE FOR THE STRUCTURE OF COMMAND POST


Concentration of command assets as one target point for adversary


The command post structure for FINDEF was following old command post centric architecture inherited from II WW times. The staff officers, facilities and staff tools were co-located in the same camp creating one target point. Command post was slow to relocate, and every relocation affected the command and control functions availability. There were additional sites prepared and back up post assigned, but they were not in readiness to take over but with delay. 

Command post was reasonably easy to detect and identify since it had typical features notable in electromagnetic radiation, heat radiation and traffic. Since location did not change for 24 hours, a rudiment targeting process was able to detect, identify and target the command post. If the decision to fire was taken, one cheap ballistic missile with 500 kg warhead of high explosives was enough to destroy unhardened command post even with 500 m circular error probability. The simple architecture of as-is command post structure is depicted in figure 20.

Figure 20: Model for AS-IS Command Post of FINDEF before 2004

The intermediate operational level command post or headquarters would host typically between 80 – 150 staff officers and unique information that was not backed up. The loss of function would last several hours as backup headquarters would try to gain the adequate level of awareness. The loss of value for Blue Force would be non-replaceable during the same operation. There were severe single points of failure in the command structure of FINDEF as the available firepower and precision of adversary’s C2-attack capabilities improved. 


From monolithic headquarters towards command post system


During modelling, simulation and field tests in TOC-project, several variations were experienced in trying to solve the challenge of survivability. Survivability of headquarters was studied from three directions of protective means: 

  • Sheltering: Digging a fortification for all regional and above headquarters appeared to be too expensive and vulnerable to other than kinetic effects.
  • Dispersion: The culture of staff officers and staff processes were very proximity oriented. The maturity of content management was not enabling remote staff work at first hand.
  • Mobility: The pace of transporting one monolithic headquarters did not seem to be enough to happen inside the target acquisition cycle of the adversary.

Technical opportunities were studied from two lines of operation: platform-centric or network-centric. The platform-centric approach assumed that all needed assets for C2 are within the structure of command post. The approach provides three options for improved survivability: 

  1. Alternative command post indicates that there is manning and infrastructure intact if the main site is disabled. There is some delay in substituting lost function. Alternativity requires more resources and provides reliability by 1+1 model. 
  2. Substituting command post assumes that there is some other headquarters in action that can quickly absorb responsibilities of the disabled command post. Relies heavily on sharing of information and ability to reassign duties. Does not provide but the reliability of 1+1 model.
  3. Distributed command post provides survivability by residing in several sites at same time. Headquarters might be divided into tactical, main and sanctuary command posts sometimes specialized to particular tasks as logistics, planning or tactical execution. The model does provide 1+n reliability.

The network-centric command post structure assumes that communications, information processing and storing are all provided from geographically distributed “cloud” and only staff officers reside on the site of the command post. The approach provides three options to improve survivability:

  1. Lightweight headquarters concept provides more than three simultaneous command posts either actively engaged or ready to take over. Since technology is in the network, it is easier to support more command posts and transfer them with a higher pace. The model provides n+1 reliability.
  2. Transferable headquarters have smaller functional subparts that can be distributed or assembled in different variations. A subpart of 10-20 staff officers may specialise either to planning, intelligence, support, situational awareness or tactical execution. Besides n+1 reliability, the concept provides transferability that may counter the C2W target acquisition capability of the adversary.
  3. Mobile command post structure is divided into small - five staff officers – command post cells. The cells are mounted and operational also while moving. Mobility and small physical aperture provides the best protection against C2W countermeasures but calls for wide wireless bandwidths.

After few exercises with these models, it came apparent that the maturity of processes, content management and skills in using technical tools needed remarkable improvement before more distributed command post structures were introduced. 

Although, there was not maturity for linear technical development, a vision for more survivable command post structure was created. The vision is in Figure 21.

Figure 21: A model for TO-BE architecture of Command Post Structure 

Headquarters are divided into small cells of five staff officers with two support crew members. Each cell is independent in means of working, housing, moving and protection. After arrival at the connection point, the cell is camouflaged, plugged in and ready to take over within 15 minutes. The cell can be mounted in vehicles or containers. The cell may also use portable IT-devices to access to command and control services in the network. 
Each cell is specialised to some of the functions within headquarters: planning, intelligence, situation or commanding. The cell can sustain either 8- or 12-hour shift in action, and then rest and be ready to take over before being activated again. Intensive shift cycling in virtual staff work requires well-educated staff officers who are familiar with working online and in a virtual environment. There is a need to alter the traditional proximity based mind model of staff work.

The cell is a building block for composite command post that can be assembled within a fortified shelter to provide classical headquarters within the same site. Command post may also be distributed geographically and specialised in different functions. There may be logistics, operational planning and tactical execution oriented command posts within one headquarters. To enjoy the best survivability, cells may be fully distributed. Fully distributed cells are located different sites independently and moving every eight hours minimum. There are no electromagnetic fingerprints, heavy traffic or strong heat signature to be detected. Headquarters are vulnerable only to attacks in the cyber environment.


Spiral development transforms mind models and habits gradually


The TOC prototype in the Northern Command did create positive expectations for higher commanders 2001. They gave permission to proceed with concept towards the main exercise in mid-2002. The TOC provided lighter movement of staff cells from the main site to alternative site. It also enabled open collaboration between parts of same headquarters and their subordinate headquarters. The trust to the concept was established, and 2004, the major exercise in the Northern Command called for all headquarters to use TOC concept in staff work. The majority of reserve officers did adapt quickly to virtual staff working methods where some older commissioned officers faced difficulties.

The Land Forces of FINDEF was planning to improve tactical command post infrastructure from 2005 onwards and saw the opportunity of composite command post structure. After traditional armament procurement, Land Command was able to field the first containers and vehicles in their 2010 main exercise. Fortunately long procurement provided the Land Command with enough time to improve the maturity of content management, sharing culture, C2 processes and information systems. Time used well enhanced the adaptation of new method in exercise. Still, for officers with experience from the Northern Command, it was easy to fit into virtual headquarters, but the rest were feeling being slightly out of their comfort zone.

The Inspector of Signals was able to declare at the beginning of 2010 a linear development strategy for new command and control structure. By the end of 2012, the Land Forces of FINDEF had reached the required capability in survivability possible with Army Command, Control and Information System, M-12 and the maturity of Land Forces culture, processes and content management.

Next part will explain the architecture of information management

2015-12-25

Transformation of military computing; Part C of Introduction to ICT rationalization program of the Finnish Defence Forces from Enterprise Architecture viewpoints

ARCHITECTURE FOR COMPUTING INFRASTRUCTURE

This is the third part of writings in introduction to FINDEF ICT rationalization that took place between 2004 - 2008 from Enterprise Architecture viewpoint.

Evolutionary outcome of few decades of military computing


The structure of computing in FINDEF by 2004 was a result of decades of evolutionary sediments. There was Mainframe (MF) computing providing terminal sessions over remote connections. There were number of stand-alone PC’s providing platform for many special applications for individual needs. There were VAX/VMS, SUN UNIX, Windows Server, IBM OS2 and Novel Netware client-server systems build for specific information system. Since 1995 there had been efforts to standardize this infrastructure but since computing was mainly owned by military branches and Services, there was no will or resources enough behind the rationalization. Most of the computing happened in each garrison within the reach of Local Area Network (LAN). Only Mainframe and some Human Resources related information systems were centralized as depicted in Figure 16.


Figure 16: The AS-IS situation of FINDEF computing in 2004

This structure hyped with over 130 medium or bigger computing sites (over 50 users each), each hosting over 20 bigger information systems, average number for administration tasks was 3000 per site.  There were over 300 different information systems, 5500 different applications, over 600 vendors, about 10% of total personnel and about 10% of annual budget in providing information related services in FINDEF. These services were supporting mainly (75%) administrative functions and not core functions. 

The analysis of linear continuum of this evolution forecasted unpleasant future for computing of FINDEF :

  • There are no more resources to support maintaining this heterogeneous infrastructure in FINDEF
  • The lack of resources and competent personnel is hindering the improvement of network enabled defence capabilities for FINDEF
  • As the complexity of Information technology increased it might become cost-effective to out-source IT support to partners
  • The competence of personnel in FINDEF is not sufficient to maintain heterogeneous IT infrastructure as complexity is distributed in all garrisons.
  • There is no base to build interoperability between Services, with other governmental agencies, with partners or with international allies since data is scattered in hundreds of dedicated information systems
  • The FINDEF is not able to comply with requirements of Information society program by the Government of Finland.

This analysis provided enough evidence to commence the transformation and create the sense of urgency called after in Kotter’s (1996) Leading change. 


New computing architecture for FINDEF

The idea for future computing concept was to gather most of the computing inside the core network and simplify the client in terminal device to degree that it is maintainable by end user. This required continuous connectivity to core computing services. The change in information management was actually requiring different connectivity also since data was born mostly in numerous systems and collected data warehouses. This ended up that no one man was able to make sense nor make decisions disconnected.

Core computing was done in metro information powerhouses, where presentation logic, applications and databases resided. Only thin client remained in end user terminals. Information powerhouses were categorised to centralized datacenters and regional datacenters according to survivability and scalability requirements. All three core computing layers created each a network in which both availability and performance was more scalable. Just by adding storage or processing units to already distributed structure, one was able to adjust the survivability as crises evolves or performance as need for storage or processing power appears. The information powerhouses provided a common session support and standard client platform to all applications. All sessions were protected with virtual private network connection. All clients were maintained with MS system management solutions. All sessions were identified and access granted based on strong identification via smart card. All application had same presentation layer provided by portal where role based access was categorising users first time. Then the actual servers and business applications were consolidated with three different solutions within information powerhouses:

  • Data center cabinet as a service was lowest level arrangement where the server was consolidated as-is from its remote location. Only power, cooling and infrastructure management was provided by information powerhouse and its personnel. Otherwise it remained under the responsibility of original owner. This status was given to servers that had more than 3 years but less than 5 years hardware life cycle left. Presentation layer was normally terminated at second layer with Citric Metaframe so client was changed to browser based.
  • Platform as a service, where existing applications were substituted with ones that were running over provided standard platforms. Those platforms were enterprise solutions as Lotus Domino, MySAP, CISCO computer telephony integration or IBM WebSphere. The standard terminal configuration included client software for these platforms. This was provided to those systems with less than 3 years of life cycle remaining.
  • Software as a service was provided from information powerhouse to replace a number of different applications. Process owner had to choose from provided list what application she preferred and then information powerhouse provided these applications as on-demand service. Process owner was released from other responsibilities and rights concerning applications, infrastructure and their maintenance.

The TO-BE architecture for FINDEF computing infrastructure is illustrated in Figure 17.


Figure 17: The planned computing architecture for 2007 onwards in FINDEF

The migration from distributed and stove piped structure towards more centralized and flexible structure took four years and several steps in improving the competence of personnel.


Consolidation of military computing in creating flexible infrastructure for network enabled defence

Consolidation of the FINDEF computing was divided into two main courses of action depicted in Figure 18. Enterprise resource management area of military affairs was consolidated from all those information systems and networks that were categorised as administrative or supportive computing. This environment was optimized to support client-provider value chain that extended beyond the borders of FINDEF. It was also optimized for effective force production and force support. The consolidation was a migration from over 100 garrison based computing sites either to less than 10 regional sites or directly to three main data centres. Where the Application Service Provider (ASP) maturity of technology and processes were achieved, there outsourcing to Provider Partner was considered. The leading idea was that outsourcing problems before solving them at least at process level is not a long-term solution. 


Figure 18: Consolidation of the computing of FINDEF

As the consolidation of administrative information technology was phased first, there was also requirement for this program to release human resources to execute the second course of action in operational computing. This environment was heading towards integrated command and control structure where main process relationship would be supporter – supportee. It was also to enable do more with less resources as combined arms fires, joint logistics and flexible decision making.

The migration was from unit and arms specific systems towards “cloud computing” structure of about ten data centres that would provide both operational and tactical applications as service besides the organic applications hosted in each unit. This was to enable more flexible use of information in each phase of operation and readiness of defence. Thus Air, Navy and Land command and control systems were hosted AS-IS in operational data centres being forced to exchange data via joint level command and control system. Surveillance and Reconnaissance systems were connected to operational cloud besides their parent units thus enabling the collection and fusing of multisensory picture for enemy tracks. The consolidation in operational environment was to end with separate domains for fires, command and control and sensing.

Together the two main environments for operations and support created the foundation for networked enabled defence: Value chain for both Teeth and Tail enabled with information. This end was to provide ability to use different specialized units together in mission; enable flexible cooperation with different governmental and non-governmental agencies within international context and finally achieve the strategic goal of flexibility in facing whatever surprise adversary and situation might produce.

The consolidation of computing was visible also to end user when the devices of their everyday workplaces changed. This proved right the clause of “Everybody is ready for changes, but nobody wants to change” or as Aristotle says “We are what we repeatedly do”.


Tangible results visible to all end users

The personal and branch driven evolution of electronics was visible on the table of administrative end user. The sedimentation over 10 years of personal computing was evident as each user had in average three personal computers with printers and other peripherals. He was also provided with 2-3 different telephones. He had a number of copiers, scanners and facsimiles available in his office. The maintenance and sustenance of all this electronics was overstretching both available personnel and budget. The change faced by average end user in FINDEF through 2004 – 2008 is illustrated in Figure 19.


Figure 19: Rationalization of administrative ICT devices provided to end user through 2004 – 2008

The biggest change was provided when Internet workstation was replaced by Internet as a service within administrative workstation. This was done in information powerhouses where 30 000 Internet users were terminated with Citrix metaframe and the connection was provided as a service to all administrative users. Since operational environment was providing a special laptop computer for mobility, all administrative PC’s were consolidated into one machine with either 5 years lifecycle provided by C4I Agency or 3 year lifecycle provided by a leasing company. As computers were replaced either within 3 or 5 years FINDEF also got rid of unnecessary busy work during updates of major operating system and excess on-site support.

The other bigger change was the centralization of printing, scanning, copying and faxing. This was again provided as a service by C4I Centre with good support of partner. All peripheral devices were consolidated into department or unit centred multifunctional machines. Costs was transformed from fixed to flexible so expense was only from usage rather than investment. Service was provided as turn-key solution including papers, ink, cartridges and maintenance. It affected about 14 000 users and replaced about 9 000 different peripherals with 2 000 multipurpose machines.
  
Telephony service was also rationalized since average user was not utilizing the added services provided by fixed digital ISDN phone. Together with ISDN-phone the large network of ISDN branch exchanges was also dismantled. More modern mobile telephony service provided by a partner was decided to use for military administrative purposes. Only a small number of analogue telephones was to remain for providing special needs. Operational telephony users were provided with TETRA services and computer integrated collaboration applications in their laptops.

Since end user changes do create the biggest opposition there was important to get the highest level sponsorship behind these transformations. The commander of FINDEF together with all Generals were the first to use new services thus showing example to all personnel. Chief Information Officers in each Service were leading training and awareness sessions and made themselves the “super users” of new devices and IT services showing hands-on to the personnel the example in improving every day knowledge work.

This ends the third part focusing on transformations in computing architecture. The next part is describing the changes in command post architecture of FINDEF.